AI Agents in the Cloud: Who Holds the Keys When You Look Away
Tip ...
Tip ...
Tip ...
Info ...
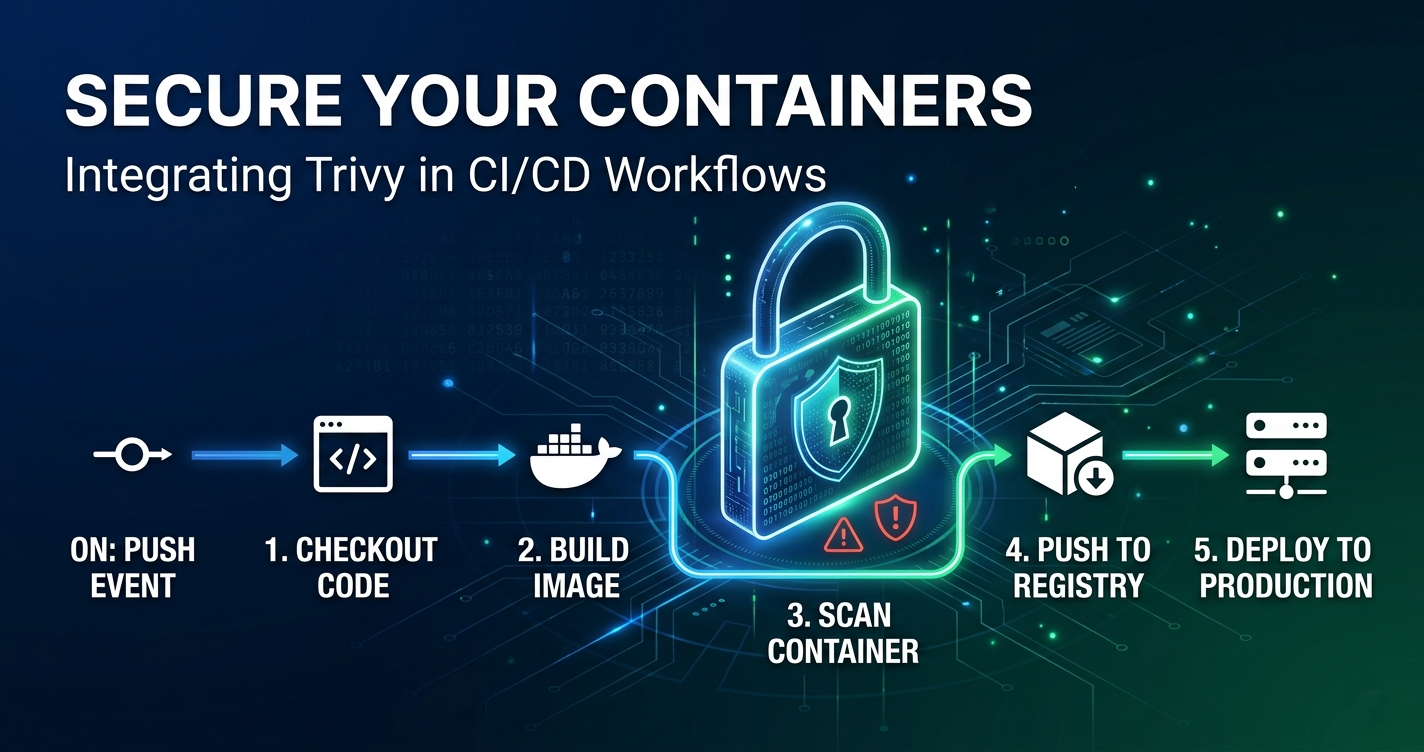
This hardening effort was directly triggered by the recent Trivy supply chain compromise, which impacted some repositories in my workplace. That prompted a full review of my own repository controls. If you want more information about the incident and the response, the following two links are worth reading first: Incident analysis: Trivy Compromised a Second Time (StepSecurity) Official disclosure and remediation guidance: Aqua Security discussion #10425 The aim of my actions to my repository was not to chase perfect security. It was to put in place some practical controls that are easy to maintain and that reduce real risk in day-to-day development. ...
I was hardening this blog’s GitHub repository as part of a security series — adding CodeQL static analysis, Dependabot, and secret scanning. Everything went smoothly until I tried to run CodeQL in a workflow against my personal, private repository. The workflow ran. The analysis completed. And then it failed with this: Warning: This run of the CodeQL Action does not have permission to access the CodeQL Action API endpoints. Code scanning is not enabled for this repository. The repository settings showed Code Scanning as available. The workflow had security-events: write. The YAML was valid. The workflow was not running from a fork. Nothing obvious was wrong. ...

So you were going through commits in your organisation’s repository and saw a little “Verified” badge next to the commit hash. Wondered how their commit got Verified? GitHub certainly doesn’t have a subscription that will give you a “Verified” badge like some other social media platforms. You know the one, I’m talking about. So what does it mean? How do you get that? Let’s explore. What Is Git Commit Signing? Do you remember how you configured Git on your machine? You probably ran a couple of commands like these: ...
Background In my previous role, while working in the Insurance domain, we provided a mobile app to all customers who bought cyber insurance. This had some cool value added services that helped small enterprises check if their employees’ knowledge of cybersecurity is good enough to protect the organization from being compromised. Thus, we implemented a one-click phishing campaign solution, which enabled users to click a button and initiate a phishing campaign for the organization. This was a really fun thing to work on. This was when I invested some time looking into how email really worked. ...
Background I have been wondering how to simplify the concept of handshakes - not the human handshakes; I’m talking about the computer ones, like the ones that happen between a server and a client when establishing a connection over HTTPS. So I went reading online to see if the content was digestible for everyone - including beginners. I couldn’t find a simple diagrammatic representation, so I thought maybe this is my chance to draw them and help others understand it at a glance. To be fair, it isn’t that straightforward to jump into discussing TLS handshakes, without learning about a few key terms. So I am certain that I will update this post with more information later on ...